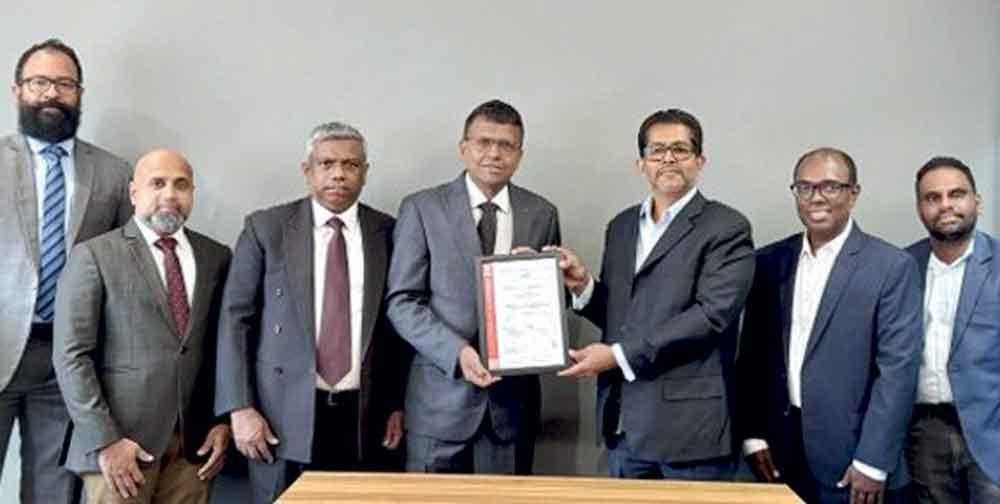
DMS Software Engineering (Pvt.) Ltd, a member of the DMS group and one of Sri Lanka’s established enterprise technology providers, has achieved the internationally recognised ISO/IEC 27001:2022 certification for the Information Security Management System, supporting its payroll services operations.
This milestone reinforces the company’s commitment to protecting sensitive information, strengthening information security governance and maintaining customer trust.
As organisations increasingly adopt outsourced and digital payroll solutions, protecting sensitive employee information has become an essential business responsibility. Beyond ensuring accurate and timely salary payments, businesses must safeguard employee confidentiality, maintain regulatory compliance and preserve trust in how payroll information is handled.
ISO/IEC 27001:2022 provides an internationally recognised framework for establishing, implementing, maintaining and continually improving an Information Security Management System. The certification demonstrates DMS’ structured approach to identifying and managing information security risks while supporting the confidentiality, integrity and availability of information within the certified scope.
DMS Software Engineering Director and General Manager T. Baheerathan said, “Achieving the ISO/IEC 27001:2022 certification reinforces the trust our customers place in DMS. We take this opportunity to thank Buddhika De Alwis and his team at Trustvault for their valuable guidance and consultation in the implementation and ongoing maintenance of our Information Security Management System.”
DMS General Manager HR Services Manju Welivitage said, “The ISO/IEC 27001:2022 certification reinforces our commitment to protecting that information and delivering payroll services with the confidentiality, security and continuity our customers expect.”
Bureau Veritas Lanka Country General Manager Shan Nanayakkara commented, “This achievement demonstrates the organisation’s commitment to managing information security risks through an internationally recognised framework and provides stakeholders with independent assurance of its structured approach to information security.”